
Memory management has always been one of the most challenging parts of systems programming. A small mistake involving a pointer, buffer, or resource can cause crashes, corrupted data, security vulnerabilities, or unpredictable program behavior. Languages that provide direct memory control often give developers considerable flexibility, but that flexibility can also create opportunities for serious programming errors.
Rust takes a different approach. It is designed to provide low-level control while using compile-time rules to prevent many common memory-related problems. Instead of depending entirely on a garbage collector or expecting developers to manually track every allocation, Rust uses ownership, borrowing, lifetimes, and strict type checking to establish how memory can be accessed.
Understanding how Rust prevents memory errors is important for anyone learning the language. These features are not simply restrictions imposed by the compiler. They form the foundation of Rust’s approach to building fast and reliable software.
Why Memory Errors Are a Serious Problem
Programs frequently create, access, modify, and release data stored in memory. When memory is handled incorrectly, the consequences can range from minor bugs to serious security problems.
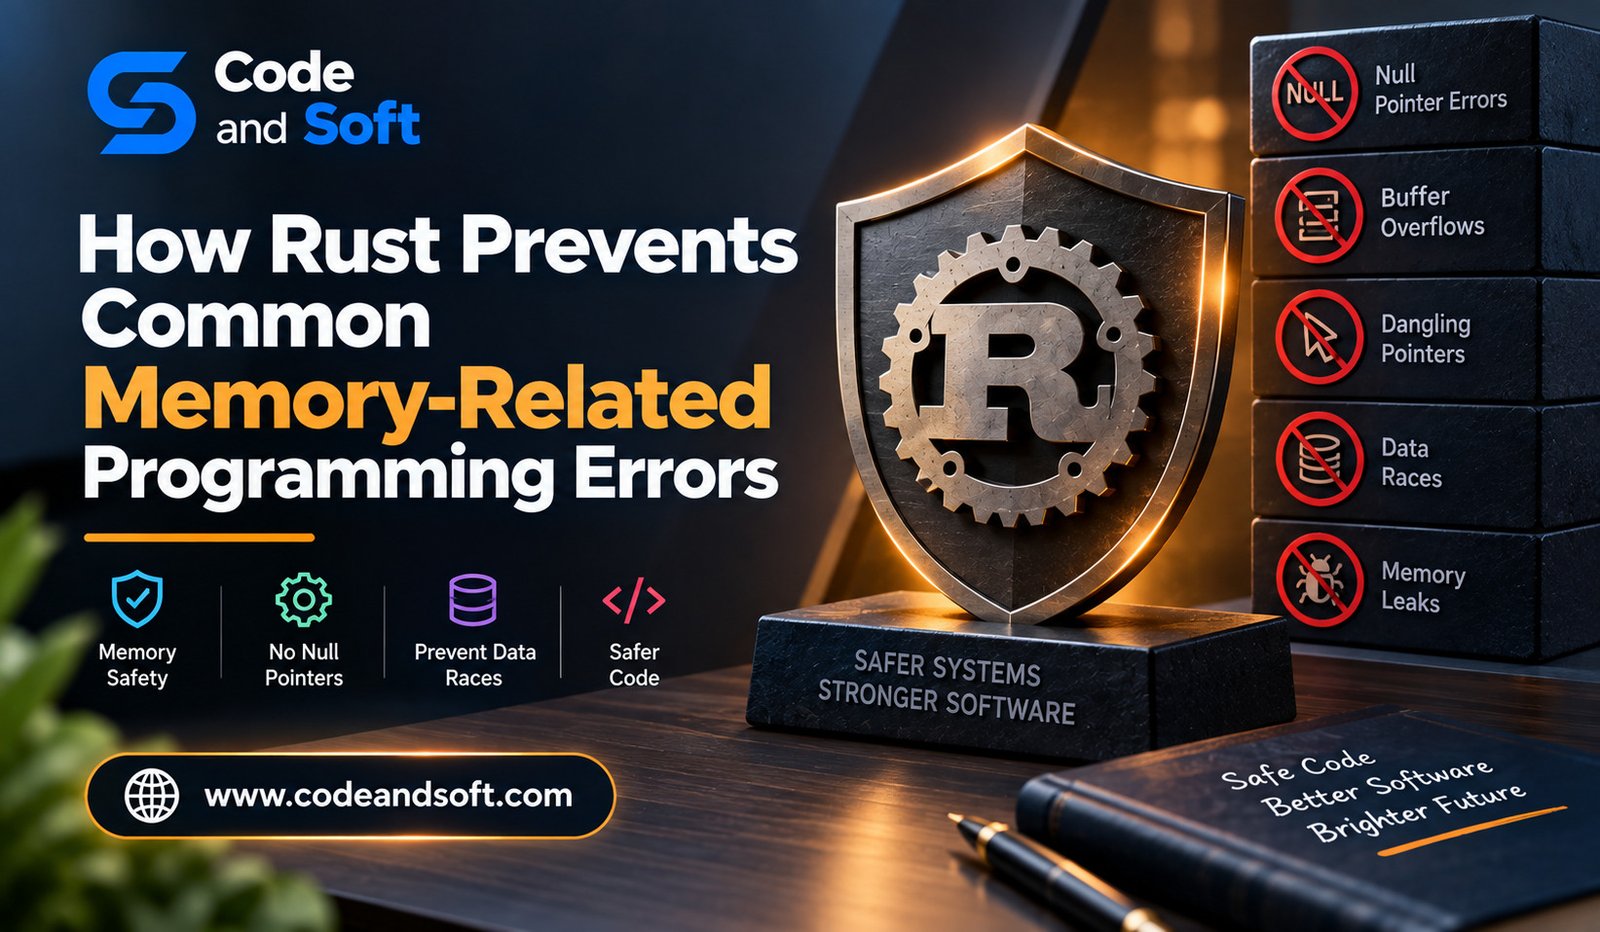
Common memory-related errors include using memory after it has been released, freeing the same memory more than once, accessing data outside a valid boundary, and allowing multiple parts of a program to modify shared data unpredictably.
These problems can be particularly difficult to identify because a program may appear to work correctly during testing and fail only under specific conditions.
Rust attempts to prevent many of these problems before the program is compiled.
Ownership Controls Who Is Responsible for Data
Rust’s ownership system is one of its most important memory-safety mechanisms.
Every value in Rust has an owner. There is normally only one owner at a time, and when that owner leaves its scope, Rust automatically cleans up the associated resource.
For example, when a String is created, the variable holding it becomes responsible for that value. When the variable goes out of scope, Rust knows that the string is no longer needed and can release its allocated memory.
This approach reduces the need for manual memory deallocation.
In languages where programmers explicitly allocate and release memory, forgetting to release an allocation can create a memory leak, while releasing it incorrectly can produce other problems. Rust’s ownership model provides a structured way to determine when resources should be cleaned up.
Rust Prevents Double-Free Problems
A double-free error occurs when a program attempts to release the same memory more than once.
This can corrupt memory management structures and potentially cause a program to crash or behave unpredictably.
Rust reduces this risk through its ownership rules. A value cannot have multiple independent owners responsible for freeing the same resource.
When ownership moves from one variable to another, the original variable is no longer considered the owner.
For example:
let first = String::from(“Rust”);
let second = first;
The ownership of the string moves to second. Rust does not allow first and second to independently clean up the same allocation.
This compile-time rule prevents an entire class of memory-management errors.
Preventing Use-After-Free Errors
A use-after-free error happens when a program attempts to access memory after that memory has already been released.
These bugs are particularly dangerous because the memory may have been reused for something else.
Rust’s ownership and borrowing rules make it difficult to create references that remain active after their underlying data has been destroyed.
Consider a reference to a local variable. When the variable goes out of scope, Rust knows that the associated data is no longer valid. The compiler rejects code that attempts to keep using a reference beyond the lifetime of its data.
This is one of the major differences between Rust and languages where pointers can continue to exist even after the memory they reference has been released.
Borrowing Provides Controlled Access
Ownership does not mean that only one part of a program can use a value.
Rust provides borrowing so that code can temporarily access data without taking ownership.
An immutable reference can be created with &, allowing data to be read without transferring ownership.
fn show_name(name: &String) {
println!(“{}”, name);
}
The function can use the string, but the caller remains its owner.
This separation between ownership and access helps Rust track which parts of a program can interact with a value.
Mutable References Prevent Conflicting Changes
Rust also provides mutable borrowing through &mut.
A mutable reference allows data to be changed, but Rust places strict limits on simultaneous access.
The language generally prevents multiple mutable references to the same value from existing at the same time. It also prevents conflicting combinations of mutable and immutable references.
This rule is important because unrestricted simultaneous access could lead to unpredictable results.
For example, imagine one part of a program reading a value while another part changes it. Without appropriate synchronization or restrictions, the reader might observe inconsistent information.
Rust’s borrowing rules identify many of these conflicts during compilation.
Preventing Data Races
Data races are a major concern in concurrent programming.
A data race can occur when multiple threads access the same memory at the same time, at least one access modifies the data, and the accesses are not properly synchronized.
Rust’s type system and ownership model make many common data races impossible in safe Rust.
When data is shared between threads, Rust requires the programmer to use mechanisms that satisfy the language’s safety rules. Types and synchronization tools help establish whether sharing particular data is safe.
This means developers cannot simply assume that concurrent code is safe because it compiles in another language.
Rust’s compiler becomes part of the process of checking whether data can be shared safely.
Bounds Checking Helps Prevent Invalid Memory Access
Another common memory-related problem is accessing an array or collection outside its valid range.
Suppose a program attempts to access an element that does not exist. In languages with unrestricted memory access, this can potentially lead to reading or writing unrelated memory.
Rust performs bounds checking for normal array and slice indexing.
For example:
let values = [10, 20, 30];
println!(“{}”, values[5]);
Rust detects that the requested index is outside the valid range. Rather than silently accessing arbitrary memory, the program fails in a controlled manner.
This protection is especially important when working with input whose size cannot be predicted in advance.
Lifetimes Keep References Valid
Ownership and borrowing are closely connected to Rust’s lifetime system.
A lifetime represents the period during which a reference is valid. Rust’s compiler analyzes relationships between references and the data they point to.
One important goal is to prevent dangling references.
A dangling reference would point to memory that is no longer valid. Rust’s compiler rejects code where a reference could outlive the data it references.
Beginners may encounter lifetime annotations when working with more complex functions or data structures. Although lifetime syntax can initially seem complicated, the underlying purpose is straightforward: references must remain connected to valid data.
Rust Reduces Memory Leaks, But Does Not Eliminate Every Leak
Rust’s ownership system automatically releases many resources when they go out of scope, which helps prevent traditional memory leaks.
However, it is important to understand that Rust does not make every possible memory leak impossible.
Certain programming patterns can intentionally or unintentionally keep data alive longer than necessary. Reference-counted structures can also create cycles that prevent automatic cleanup.
Rust therefore provides strong memory-safety guarantees without claiming that developers never need to think about resource usage.
The language makes common mistakes harder to create, but good software design remains important.
Unsafe Rust and Developer Responsibility
Rust includes an unsafe feature that allows developers to perform operations that cannot be fully verified by the compiler.
Unsafe code can be useful for interacting with hardware, foreign-language interfaces, operating-system APIs, or highly optimized low-level components.
However, entering an unsafe block means that additional responsibility falls on the programmer.
The important distinction is that Rust does not remove low-level programming capabilities. Instead, it separates operations that the compiler can automatically verify from operations that require greater developer control.
This balance allows Rust to remain suitable for systems programming while keeping most application code inside the safer part of the language.
Why Rust’s Memory Safety Approach Matters
Rust’s approach is significant because it combines memory safety with performance.
Garbage-collected languages can automatically manage memory, but garbage collection introduces a different set of runtime considerations. Manual memory management provides control but places more responsibility on developers.
Rust attempts to achieve a middle ground by moving many memory-safety checks into compilation.
Developers can still work close to the hardware, control data structures, and build performance-sensitive applications while receiving strong protection against common memory errors.
Final Thoughts
Rust prevents many common memory-related programming errors through a combination of ownership, borrowing, lifetimes, type checking, and bounds checking.
Its compiler checks how values are moved and accessed, determines whether references remain valid, and identifies many potentially unsafe patterns before the program runs. These rules help prevent problems such as double frees, use-after-free errors, dangling references, conflicting data access, and many data races.
Learning Rust therefore involves more than memorizing syntax. It means understanding how the language models memory and why its compiler enforces particular rules.
Once these concepts become familiar, Rust’s restrictions start to feel less like obstacles and more like tools for building dependable software. That combination of memory safety, performance, and low-level control is one of the main reasons Rust has become an important language for modern systems programming.